OpenWRT opens SSH port for the whole world
How I noticed
Because of my pihole snatching all remaining ipv4 addresses from my DHCP Server (main router with openWRT), I thought of checking the log would be a good Idea. In logs I did not only find the entries regarding DHCP but also a lot entries like this:
[Aug 16, 2026, 20:02:30 GMT+2] authpriv.info: dropbear[31812]: Child connection from 91.92.40.43:11952
[Aug 16, 2026, 20:02:30 GMT+2] authpriv.info: dropbear[31812]: Exit before auth from <91.92.40.43:11952>: Exited normally
And I thought, that this can't be good. An external IP address not being mine trying to authenticate via dropbear (SSH server). So I duckduckgoed, asked in my signal groups and asked AI, but I did not really get an answer why this is, “just” some hints how to test if SSH is opened for the whole world.
How I found the reason
As I did not get any meaningful help, I checked the port forwards and traffic rules in openWRT (Network –> Firewall –> Port Forwards / Traffic Rules)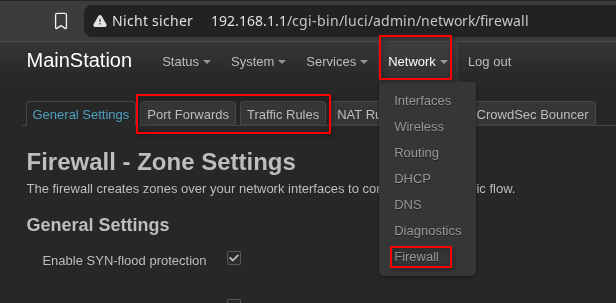 ,but did not find anything related to SSH / Port 22 also. This was a bit frustrating and I check the firewall overview. And again nothing. But I guess I was just blind, because here should be listed everything related to traffic ;). So I simply clicked through all the menu items, tabs and so on, until I found one thing called “SSH Access” within Admin menu.
The Problem
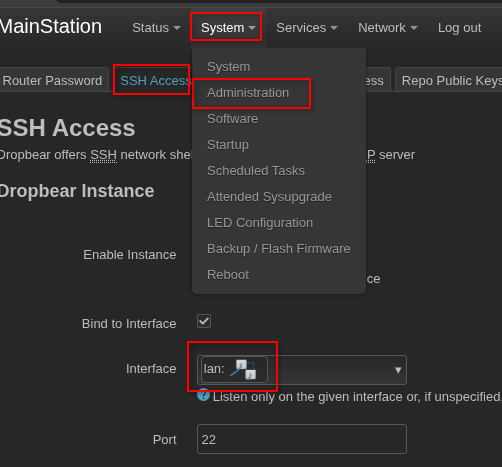
It is no real problem but a configuration, I guess I messed up at initial installation. You can enable SSH access to the router and tell it on which interface it should listen. If you do not select any interface, it listens to every interface. So the interface to the outside world is included.
The Solution
In my case I only need access from within my local network. So I could simply change the interface to my local one. And that's it :D
#Edit
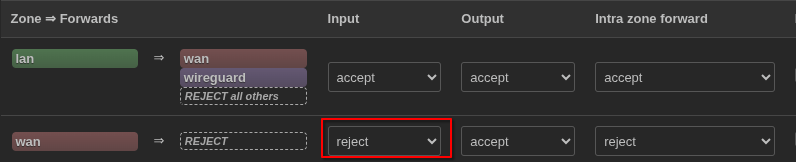
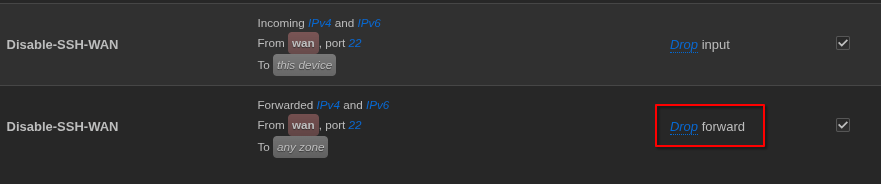
I got a hint, that I can let the SSH Access set to all interfaces and in the firewall zone for WAN I should drop or reject input traffic. I also got a traffic rule to drop SSH requests. But this was set to forward and not for input.
I changed this to following setup: